Works offline
The core Solo workflow, inspect, capture evidence, report, verify, needs no cloud round-trip.
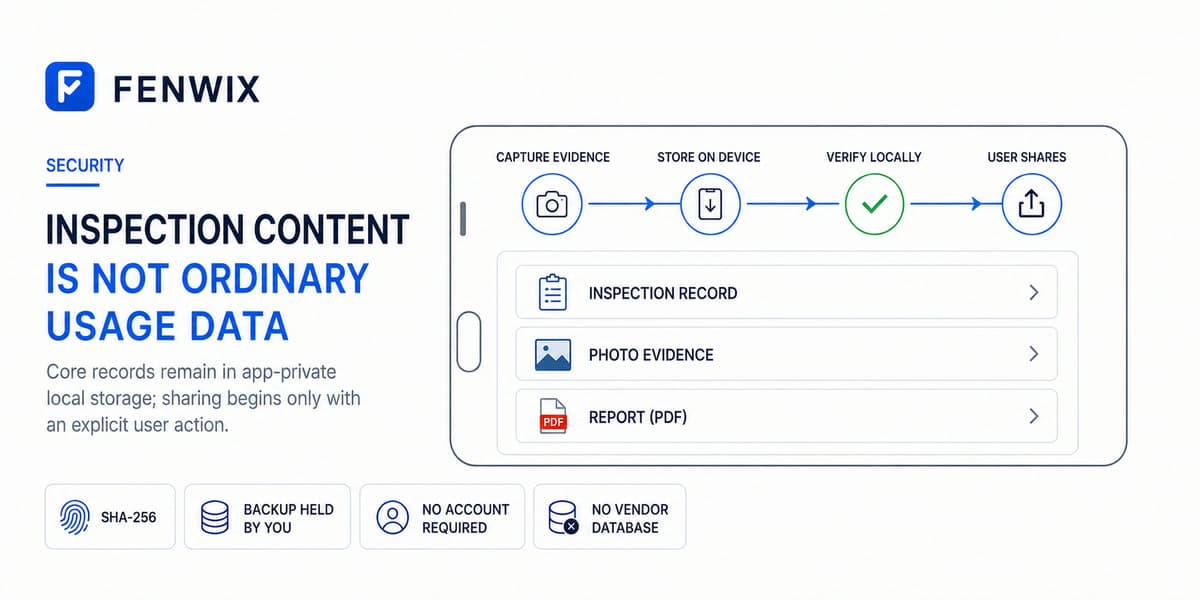
Fenwix keeps core field records in encrypted app-private local storage, makes every portable output an explicit user action and excludes inspection content from product analytics payloads. Current controls and future enterprise architecture are labeled separately at Fenwix Trust & Technology.
The core Solo workflow, inspect, capture evidence, report, verify, needs no cloud round-trip.
Fenwix stores its local database and evidence-vault objects encrypted in the application's private storage and does not require a vendor-hosted inspection database.
The core workflow runs without creating any account.
Reports and exports leave Fenwix private storage only through an action you start, such as Save, Share or Full Export. Support messages are sent only when you write and send them.
Photos are SHA-256 hashed at write time with their capture source recorded. Originals are never overwritten by annotations.
Completed inspections are corrected through revisions with a mandatory reason, never silently rewritten.
Report QR codes verify against the source record on the device, including a recheck of linked photo files.
Full export covers records, photos, audio and signatures. You hold the backup. There is no Fenwix cloud copy.
Product analytics never include site names, asset names, finding text, report content or people's names.
For architecture, Zero-Custody direction and technical trust details, visit Fenwix Trust & Technology.
fenwix.net →